Cert-Gen

Certificate Generator. 인증서 생성기.

웹브라우저의 주소 표시줄에 자물쇠 표시를 만들어주는 그것.
자세한 내용은 여기를 보면 된다.

기본적으로 인증서 발급 기관을 통해서 Server용 인증서를 발급받지만 사내 도메인을 사용하거나, 폐쇄망의 환경에서는 자체 서명/발급 인증서를 사용한다.

보통의 경우는 여기의 내용처럼 openssl 어쩌구 명령을 수차례 날려야 하기에 매우 귀찮아서 조금이라도 쉽게 인증서 생성 과정을 처리해보고자 만든 도구다.

Github 바이너리 링크

Linux(Redhat, Debian, Ubuntu)와 Windows(10,11, Server 2019이상)을 지원한다.
Windows Defender에서 트로이목마로 인식하므로, 허용해서 쓰면 된다.

사용법

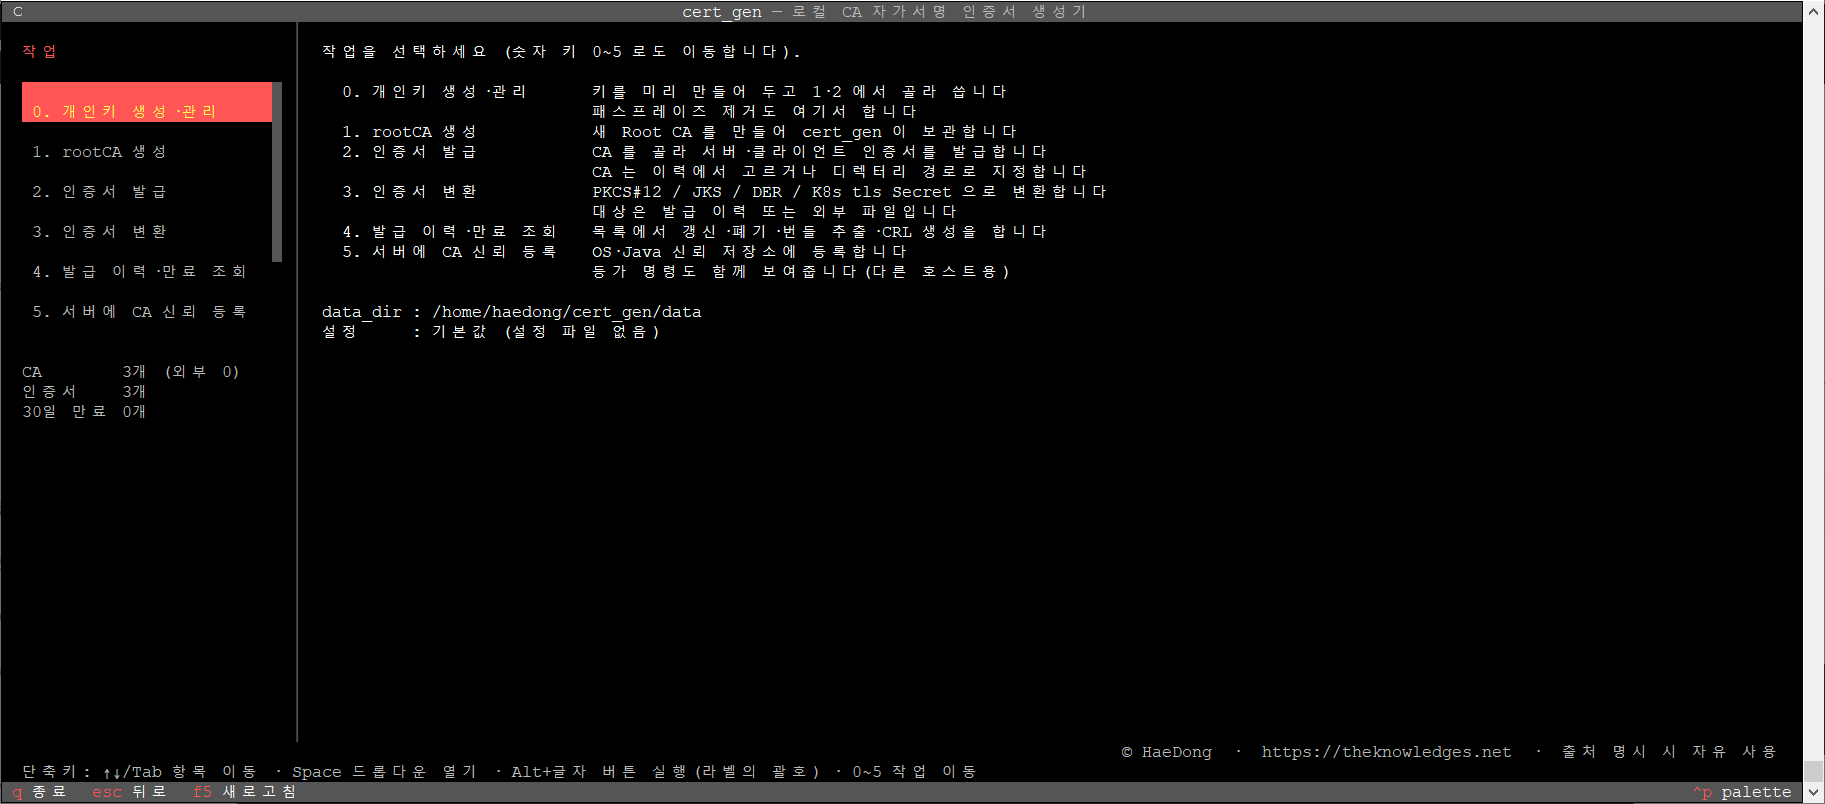
cert-gen tui
Terminal Ui를 이용해 작업한다.

haedongg.net:~/cert-gen]#    ./cert-gen --help

cert-gen 0.1.0 — 자가서명 인증서 생성기 (로컬 CA)

사용법:
  cert-gen [전역 옵션] <명령> [하위 명령] [옵션]

전역 옵션:
  --data-dir DIR    상태 디렉터리 (기본: <현재 디렉터리>/cert-gen-data)
  -c, --config FILE 설정 파일 (기본: <상태 디렉터리>/config.toml)
  --json            결과를 JSON 으로 출력
  -q, --quiet       사람이 읽는 출력을 생략
  -v, --version     버전 출력

명령:
  init                         상태 디렉터리와 DB 를 만든다
  where                        상태 디렉터리 위치와 규칙을 보여 준다
  doctor                       환경 점검 (권한·DB·CA·만료·CRL·openssl). --deep 으로 번들 해시까지

  key create --name NAME       개인키를 만들어 둔다 (CA·발급에서 고를 수 있다)
  key list                     개인키 목록 (쌍 토큰으로 인증서와 짝을 맞춘다)
  key show NAME                개인키 상세·사용처
  key import --file FILE        외부 개인키를 가져온다
  key passphrase NAME          패스프레이즈 설정/제거(--remove)
  key delete NAME              개인키 삭제 (쓰이는 중이면 거부)

  ca create                    Root CA 를 만든다 (--cn 필수, --org/--ou/--country)
  ca list                      CA 목록
  ca show SLUG                 CA 상세
  ca export SLUG               ca.crt 를 내보낸다 (클라이언트 신뢰 등록용)
  ca adopt --dir DIR           외부 CA 를 복사 없이 등록해 발급에 쓴다
  ca import --key K --cert C   외부 CA 를 상태 디렉터리로 복사해 등록한다

  apply FILE...                openssl .cnf 를 읽어 CA 생성·발급을 한 번에
                               (한 파일에 --- 로 블록을 나누거나, 파일을 여러 개 주거나)

  cert issue                   인증서를 발급한다 (--config 로 openssl .cnf 입력 가능)
  cert list                    발급 이력
  cert show REF                상세 (ID | serial | CN)
  cert renew REF               갱신 (기본: 새 키)
  cert revoke REF              폐기하고 CRL 을 다시 만든다
  cert verify REF              검증 (체인·호스트명·폐기)
  cert bundle REF              번들 zip 을 꺼낸다

  csr create                   외부 CA 제출용 CSR 을 만든다
  csr sign --csr FILE          받은 CSR 을 우리 CA 로 서명한다

  export p12 REF               PKCS#12
  export jks REF               Java KeyStore
  export der REF               DER
  export pem REF               PEM (cert/key/fullchain/ca)
  export k8s REF               kubernetes.io/tls Secret (+ Ingress)

  crl generate SLUG            CRL 을 다시 만든다
  crl list SLUG                폐기 목록

  backup create                상태 디렉터리 전체를 tar.gz 로 묶는다 (CA 개인키 포함)
  backup restore FILE          백업을 복원한다 (--dry-run 으로 먼저 확인)

  trust show [SLUG]            OS·Java 신뢰 저장소 등록 명령을 만든다
  tui                          터미널 UI 를 띄운다

비밀값은 명령행 인자로 받지 않는다 (/proc/<pid>/cmdline 노출).
환경변수나 --*-stdin 옵션, 또는 TTY 프롬프트를 쓴다.
  CERT_GEN_CA_PASSPHRASE, CERT_GEN_EXPORT_PASSWORD, CERT_GEN_KEY_PASSPHRASE

'cert-gen <명령> -h' 로 각 명령의 옵션을 본다.

SSH Tunneling

  • SSH(Secure Shell): 프로토콜을 이용하여 네트워크 트래픽을 암호화된 통로(터널)를 통해 안전하게 전송하는 기술
  • 일반적인 Proxy의 연결 방식과 차이가 없지만 SSH 프로토콜을 기반으로 작동하므로, 평문 연결에 대해서도 암호화 통신을 하는 효과를 얻을 수 있다. 단, 터널 제한을 하지 않는다면 클라이언트에서 중계서버에서 접근 가능한 모든 서버에 접근할 수 있다는 이야기이므로 오히려 보안상 취약할 수 있다.

  • 터널링 설정 : Linux Shell / Windows Power shell / OS X shell
# ssh -L $LOCALHOST_LISTEN_PORT:$TARGET_HOST:$TARGET_PORT $USER_NAME@TUNNEL_SERVER
# ssh -L 내_PC에서_오픈할_포트:실제_접속할_서버_호스트:실제_접속할_서버_포트    중계서버_계정@중계서버_호스트
ssh   -L    18080:172.17.0.100:8080    user@172.17.200.200
  • 터널링 설정 : Windows Putty

OpenLdap 설치 (on Redhat linux)

  • LDAP 개요

  • LDAP(Lightweight Directory Access Protocol) :
    디렉터리 서비스(Directory Service)에 접근하고 관리하기 위한 표준 프로토콜로써 다음과 같은 특징을 가진다.

경량 프로토콜 : 이름 그대로 “Lightweight”, 기존 X.500 디렉터리 서비스의 복잡한 구조를 단순화해 TCP/IP 환경에서 효율적으로 동작한다.
계층적 구조(Tree 구조):
dc=example,dc=com과 같은 도메인 기반 트리 구조로 데이터를 저장.
ou=users,dc=example,dc=com (ou=Organizational Unit).
데이터 저장 방식: 사용자 정보(UID, 이름, 비밀번호, 메일 등)를 속성(attribute) 형태로 저장.
검색 및 인증 서비스: SSO, RBAC 등에 사용 (OpenLDAP / Active Directory)

docker를 이용한 openVPN 설정

컨테이너가 아닌 네이티브 설치는 다음 포스트를 참조
openVPN 서버구축 #1. 개요
openVPN 서버구축 #2. 서버 설치 및 설정

docker-compose.yaml 생성

version: '2'
services:
  openvpn:
    cap_add:
     - NET_ADMIN
    image: kylemanna/openvpn
    container_name: openvpn
    ports:
     - "1194:1194/udp" 
    restart: always
    volumes:
     - ./openvpn-data/conf:/etc/openvpn #.openvpn-data/conf 디렉토리를 생성해야 한다.

설정파일 및 인증서 초기화

docker-compose run --rm openvpn ovpn_genconfig -u udp://VPN.YOUR_HOST.NAME

# 아래는 수행 결과
reating network "vpn_default" with the default driver
Pulling openvpn (kylemanna/openvpn:)...
....중략....
Creating vpn_openvpn_run ... done
Processing PUSH Config: 'block-outside-dns'
Processing Route Config: '192.168.254.0/24'
Processing PUSH Config: 'dhcp-option DNS 8.8.8.8'
Processing PUSH Config: 'dhcp-option DNS 8.8.4.4'
Processing PUSH Config: 'comp-lzo no'
Successfully generated config
Cleaning up before Exit ...
docker-compose run --rm openvpn ovpn_initpki

# 아래는 수행 결과
Creating vpn_openvpn_run ... done

init-pki complete; you may now create a CA or requests.
Your newly created PKI dir is: /etc/openvpn/pki

Using SSL: openssl OpenSSL 1.1.1g  21 Apr 2020

Enter New CA Key Passphrase: CA_KEY의_Passphrase
Re-Enter New CA Key Passphrase: CA_KEY의_Passphrase
Generating RSA private key, 2048 bit long modulus (2 primes)
................................+++++
......................................................+++++
e is 65537 (0x010001)
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Common Name (eg: your user, host, or server name) [Easy-RSA CA]:vpn.haedongg.net

CA creation complete and you may now import and sign cert requests.
Your new CA certificate file for publishing is at:
/etc/openvpn/pki/ca.crt

Using SSL: openssl OpenSSL 1.1.1g  21 Apr 2020
Generating DH parameters, 2048 bit long safe prime, generator 2
This is going to take a long time
..............................................................+...........................................+..........................................................
...중략...
........................................................+..+....................+................................................................+....+..++*++*++*++*

DH parameters of size 2048 created at /etc/openvpn/pki/dh.pem

Using SSL: openssl OpenSSL 1.1.1g  21 Apr 2020
Generating a RSA private key
.............+++++
............................+++++
writing new private key to '/etc/openvpn/pki/easy-rsa-74.akeLei/tmp.JBdIKe'
-----
Using configuration from /etc/openvpn/pki/easy-rsa-74.akeLei/tmp.BfJlok
Enter pass phrase for /etc/openvpn/pki/private/ca.key:
Check that the request matches the signature
Signature ok
The Subject's Distinguished Name is as follows
commonName            :ASN.1 12:'vpn.haedongg.net'
Certificate is to be certified until Jul 30 00:51:51 2025 GMT (825 days)

Write out database with 1 new entries
Data Base Updated

Using SSL: openssl OpenSSL 1.1.1g  21 Apr 2020
Using configuration from /etc/openvpn/pki/easy-rsa-149.FPcifA/tmp.cjaMHC
Enter pass phrase for /etc/openvpn/pki/private/ca.key: 위_11_12_라인에서_입력했던_Passphrase

An updated CRL has been created.
CRL file: /etc/openvpn/pki/crl.pem

디렉토리 권한 변경

sudo chown -R $(whoami): ./openvpn-data

서버 프로세스 실행

docker-compose up -d openvpn

클라이언트 사용자 생성 및 인증서 생성

# 비밀번호화 함께 생성
docker-compose run --rm openvpn easyrsa build-client-full 사용자_이름

# 비밀번호 없이 생성
docker-compose run --rm openvpn easyrsa build-client-full 사용자_이름 nopass

# 인증서 파일 출력, 이 파일을 클라이언트 사용자에게 전달하면 된다.
docker-compose run --rm openvpn ovpn_getclient 사용자_이름 > 사용자_이름.ovpn

클라이언트 사용자 제거

# Keep the corresponding crt, key and req files.
docker-compose run --rm openvpn ovpn_revokeclient $CLIENTNAME

# Remove the corresponding crt, key and req files.
docker-compose run --rm openvpn ovpn_revokeclient $CLIENTNAME remove

HAproxy 를 이용한 로드밸런싱 고가용성 구성

개요

HAProxy는 여러 서버에 대해 요청을 확산시키는 TCP 및 HTTP 기반 애플리케이션들을 위해 고가용성 로드밸런서와 리버스 프록시를 제공하는 자유-오픈 소스 소프트웨어이다. C 프로그래밍 언어로 개발되어 있으며 빠르고 효율적인 것으로 유명하다.
공식 사이트 참조

설정에 따라 Server #A와 #B로 번갈아가며 연결해준다.

haproxy를 통해 부하를 분산하는 등의 용도로 서비스 효율을 높일 수 있다.

설치

여기에서 다운 받아도 되며, yum epel-release에 포함되어 있으므로 epel-release 리포지터리 추가 후 yum 이나 dnf 명령 등을 통해 설치할 수 있다.

sudo dnf install -y haproxy
마지막 메타자료 만료확인 7:58:42 이전인: 2022년 07월 28일 (목) 오전 12시 23분 23 초.
종속성이 해결되었습니다.
================================================================================
 꾸러미          구조           버전                    레포지터리         크기
================================================================================
설치 중:
 haproxy         x86_64         1.8.27-4.el8            appstream         1.4 M

연결 요약
================================================================================
설치  1 꾸러미

총계 내려받기 크기: 1.4 M
설치된 크기 : 4.2 M
...중략...
설치되었습니다:
  haproxy-1.8.27-4.el8.x86_64                                                                                                                   
완료되었습니다!

서비스가 구동 될 모든 서버에 설치해준다.
자동으로 서비스가 구동될 수있도록 서비스를 등록 해준다.

sudo systemctl enable haproxy.service
 또는
sudo service haproxy start

설정

기본적으로 /etc/haproxy/haproxy.cfg 가 존재한다.

global
    log         127.0.0.1 local2
    chroot      /var/lib/haproxy
    pidfile     /var/run/haproxy.pid
    maxconn     4000
    user        haproxy
    group       haproxy
    daemon

    # turn on stats unix socket
    stats socket /var/lib/haproxy/stats

#---------------------------------------------------------------------
# common defaults that all the 'listen' and 'backend' sections will
# use if not designated in their block
#---------------------------------------------------------------------
defaults
    mode                    http
    log                     global
    option                  httplog
    option                  dontlognull
    option http-server-close
    option forwardfor       except 127.0.0.0/8
    option                  redispatch
    retries                 3
    timeout http-request    10s
    timeout queue           1m
    timeout connect         10s
    timeout client          1m
    timeout server          1m
    timeout http-keep-alive 10s
    timeout check           10s
    maxconn                 3000

#---------------------------------------------------------------------
# status web 설정
# haproxy 서비스 상태, 백엔드 서비스의 상태 등을 웹을 통해 확인할 수 있다.
# 필수는 아니다.
#---------------------------------------------------------------------
listen hastats
    mode http
    bind *:8088
    stats enable
    stats show-legends
    stats uri /hastat
# 서버 주소가 192.168.0.1이라면  http://192.168.0.1/hastat으로 접속한다.
    stats auth admin:admin
#  hastats 웹에 접속 시 인증으로 제한하려면 계정과 패스워드를 지정한다.

#---------------------------------------------------------------------
# 프론트 엔드 설정
# 프론트 엔드에서 설정한 포트로 연결이 들어올 경우 백엔드로 보낸다
#---------------------------------------------------------------------
# 외부에서 haproxy를 통해 연결을 시도할 때 사용하는 포트
frontend  kubeproxy
    bind *:16443
    default_backend kubeproxy
    mode tcp

#---------------------------------------------------------------------
# 백엔드 설정
# 프론트엔드에서  defaultbackend 타겟으로 설정 된 백엔드 정보
#---------------------------------------------------------------------
backend kubeproxy
    balance     roundrobin
# Balance Option
# Roundrobin : 순차적으로 분배
# static-rr : 서버에 부여된 가중치에 따라서 분배
# leastconn : 접속수가 가장 적은 서버로 분배
# source : 운영중인 서버의 가중치를 나눠서 접속자 IP 해싱(hashing)해서 분배
# uri : 접속하는 URI를 해싱해서 운영중인 서버의 가중치를 나눠서 분배 (URI의 길이 또는 depth로 해싱)
# url_param : HTTP GET 요청에 대해서 특정 패턴이 있는지 여부 확인 후 조건에 맞는 서버로 분배 (조건 없는 경우 round_robin으로 처리)
# hdr : HTTP 헤더에서 hdr(<name>)으로 지정된 조건이 있는 경우에 대해서만 분배 (조건없는 경우 round robin 으로 처리)
# rdp-cookie : TCP 요청에 대한 RDP 쿠키에 따른 분배
    mode tcp
    option tcp-check
    option tcplog
# 외부에서 16443 포트로 연결을 시도하면 아래의 서버에 순차적으로 연결해준다.
    server  storage01 192.168.0.1:6443 check
    server  storage02 192.168.0.2:6443 check
    server  storage03 192.168.0.3:6443 check

frontend web-console
        bind *:18080
        default_backend web-console
        mode tcp
backend web-console
        balance roundrobin
        mode    tcp
        option  tcp-check
        option  tcplog
        server  storage01       192.168.1.1:8080       check
        server  storage02       192.168.1.2:8080       check
        server  storage03       192.168.1.3:8080       check

백엔드로 동작할 모든 서버에 동일한 설정 파일을 넣어준다.

확인

haproxy 웹 서비스를 통해 정보 확인이 가능한다.

백엔드 서비스에 문제가있다면 붉은색으로 표시된다.

SSL/TLS 자체 서명 (Self-signed) 인증서 생성

먼저 SSL의 개념을 이해하기 위해 SSL 그리고 HTTPS 포스트를 참고하자.

이 포스트에서 설명하는 것은 바로 ‘신뢰할 수 있는 3자’의 역할을 스스로 하는 법이다.
물론 이렇게 생성한 인증서는 root-ca에 등록된 인증서가 아니므로 웹 브라우저에서는 신뢰할 수 없는 인증서라는 메시지를 띄울 것이지만 인트라넷 환경이라거나 인증서 발급 비용이 부담1물론 Let’s encrypt 등 무료로 인증서를 발급해주는 기관도 있다. 되는 경우 자체 서명 인증서를 이용하여 https 서비스를 제공할 수 있게 된다. 적어도 http에 비해 보안성을 향상 시킬 수 있다.

준비
openssl 패키지가 필요하다. 아래 두 가지 방법으로 설치 여부 확인이 가능하다.

haedong@haedong:~:]$ rpm -qa | grep openssl
openssl-libs-1.0.2k-19.el7.x86_64
openssl-1.0.2k-19.el7.x86_64
haedong@haedong:~:]$ yum list installed |grep  openssl
openssl.x86_64                     1:1.0.2k-19.el7                 @anaconda
openssl-libs.x86_64                1:1.0.2k-19.el7                 @anaconda

만약 설치 되어있지 않으면 “sudo yum install openssl” 명령으로 설치하자.

인증서를 생성하는 과정은 “개인키 발급” ->”인증요청서 작성” -> “인증 요청” -> “발급”2여기서의 발급은 당연히 파일의 생성이다. 의 과정을 거친다.

개인키 생성

haedong@haedong:~:]$ openssl genrsa -des3 -out server.key 2048
Generating RSA private key, 2048 bit long modulus
......................................................+++
............................................................+++
e is 65537 (0x10001)
Enter pass phrase for server.key:
Verifying - Enter pass phrase for server.key:
haedong@haedong:~:]$ ll
합계 4
-rw-rw-r-- 1 haedong haedong 1743  8월 18 09:02 server.key

개인키 Passphrase 제거
생성된 개인키의 권한 확인을 위한 것으로 이 개인키로 생성된 인증서를 사용하는 서비스는 구동 시 매번 패스워드를 물어본다. 어차피 이 passphrase가 있건 없건 SSL 서비스를 제공하는데엔 아무런 문제도, 차이도 없다.

haedong@haedong:~:]$ cp server.key server.key.original
haedong@haedong:~:]$ openssl rsa -in server.key.original -out server.key
Enter pass phrase for server.key.original:
writing RSA key
haedong@haedong:~:]$ ll
합계 8
-rw-rw-r-- 1 haedong haedong 1675  8월 18 09:06 server.key
-rw-rw-r-- 1 haedong haedong 1743  8월 18 09:06 server.key.original

인증 요청서 생성

haedong@haedong:~:]$ openssl req -new -key server.key -out server.csr
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [XX]:KR                                    <- 국가코드
State or Province Name (full name) []:SEOUL                             <- 도/특별시/광역시
Locality Name (eg, city) [Default City]:GANGNAMGU                       <- 시/군/구
Organization Name (eg, company) [Default Company Ltd]:HaeDong           <- 조직,회사 이름
Organizational Unit Name (eg, section) []:INFRASECU                     <- 팀 이름
Common Name (eg, your name or your server's hostname) []:haedong.net    <- 서버, 사이트 이름
Email Address []:haedonggang@naver.com                                  <- 관리자 E-mail

Please enter the following 'extra' attributes
to be sent with your certificate request
A challenge password []:                                                <- Enter로 넘겨도 무방
An optional company name []:                                            <- Enter로 넘겨도 무방
haedong@haedong:~:]$ ll
합계 12
-rw-rw-r-- 1 haedong haedong 1066  8월 18 09:14 server.csr
-rw-rw-r-- 1 haedong haedong 1675  8월 18 09:06 server.key
-rw-rw-r-- 1 haedong haedong 1743  8월 18 09:06 server.key.original

인증서 발급 (생성)
여기서의 인증서는 원래 ‘root-ca’기관에서 발급을 해주는 인증서를 말한다. 하지만 앞 단락에서 이야기 한 것처럼 이 과정은 내가 나 스스로에게 인증서를 요청하고 인증서를 발급 해주는 것이다. 즉 root-ca에서 인증서를 발급 받는 경우는 위에서 생성한 csr 파일을 root-ca로 보내고 root-ca에서 다시 crt 파일을 보내주는 과정을 거쳐야 한다.

haedong@haedong:~:]$ openssl x509 -req -days 3650 -in server.csr -signkey server.key -out server.crt
Signature ok
subject=/C=KR/ST=SEOUL/L=GANGNAMGU/O=HaeDong/OU=INFRASECU/CN=haedong.net/emailAddress=haedonggang@naver.com
Getting Private key
haedong@haedong:~:]$ ll
합계 16
-rw-rw-r-- 1 haedong haedong 1322  8월 18 09:21 server.crt
-rw-rw-r-- 1 haedong haedong 1066  8월 18 09:14 server.csr
-rw-rw-r-- 1 haedong haedong 1675  8월 18 09:06 server.key
-rw-rw-r-- 1 haedong haedong 1743  8월 18 09:06 server.key.original

위의 crt 파일이 https 적용을 위한 인증서 되시겠다.
활용하고자 하는 서비스에 적용하면 된다. 아래는 제타위키를 참고한 apache https서비스를 위한 설정 파일 수정 예.

haedong@haedong:~:]$ sudo cp server.key /etc/httpd/conf/
haedong@haedong:~:]$ sudo cp server.crt /etc/httpd/conf/
haedong@haedong:~:]$ sudo ll /etc/httpd/conf
total 60
-rw-r--r--. 1 root root 34417 Sep 20 07:41 httpd.conf
-rw-r--r--. 1 root root 13139 Feb 14  2012 magic
-rw-r--r--. 1 root root  1298 Sep 20 08:45 server.crt
-rw-r--r--. 1 root root  1679 Sep 20 08:45 server.key
haedong@haedong:~:]$ sudo vi /etc/httpd/conf
NameVirtualHost *:443
<VirtualHost *:443>
SSLEngine on
SSLCertificateFile /etc/httpd/conf/server.crt
SSLCertificateKeyFile /etc/httpd/conf/server.key
SetEnvIf User-Agent ".*MSIE.*" nokeepalive ssl-unclean-shutdown
CustomLog logs/ssl_request_log "%t %h %{SSL_PROTOCOL}x %{SSL_CIPHER}x \"%r\" %b"
DocumentRoot /var/www/html
</VirtualHost>

당연하지만 apache 뿐 아니라 http/https 프로토콜을 연결을 제공하는 모든 서비스에 적용이 가능하다.

일반적으로 ssl 또는 tls 서비스는 443 또는 8443 포트를 사용한다.